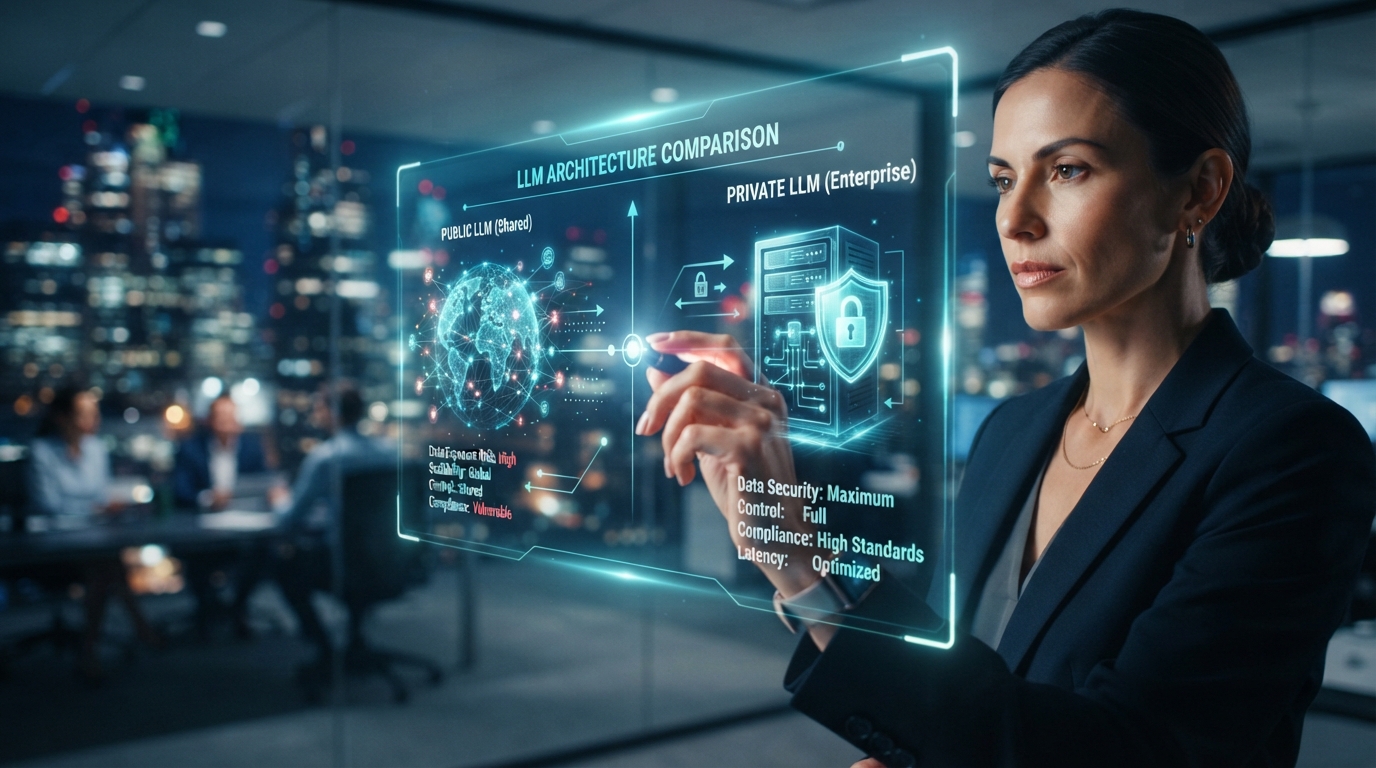
Large language models have moved from experimental pilots to core business infrastructure. Enterprises across Saudi Arabia and the wider Gulf region now use them for customer service automation, document processing, internal knowledge search, and decision support. But before scaling any AI initiative, leadership teams face a foundational question: should the organization rely on a public LLM, or invest in a private, dedicated deployment?
This is not a technical detail to be left to the IT department alone. The choice between a public LLM vs private LLM affects data governance, regulatory compliance, total cost of ownership, and how much control the organization retains over its own information. Getting it wrong can mean unnecessary spend, exposure to compliance risk, or a system that cannot scale with the business.
This guide breaks down what public and private LLMs actually are, how they differ in practice, and how CIOs, CEOs, and government technology leaders can make a defensible choice for their organization.
What Are Public and Private LLMs?
A public LLM is a general-purpose AI model hosted and operated by a third-party provider, accessed through an API or a consumer-facing interface. The provider trains the model, manages the infrastructure, and typically serves the same underlying model to many organizations simultaneously. Popular examples include widely used commercial chatbot and API services.
A private LLM, by contrast, is deployed within an environment the enterprise controls whether on-premises, in a private cloud, or in an isolated virtual private cloud (VPC) instance. The model may be a customized open-source model, a fine-tuned version of a commercial model licensed for isolated deployment, or a model built specifically for the organization's data and workflows.
The distinction is not simply "internal vs external." It comes down to three factors:
- Where the data goes does customer or operational data leave the organization's controlled environment?
- Who controls the model can the enterprise fine-tune, audit, or restrict the model's behavior?
- How access is governed does the organization set its own authentication, logging, and retention policies, or rely on a vendor's defaults?
Understanding this distinction is the starting point for any serious evaluation of public LLM vs private LLM options at the enterprise level.
Key Features of Public and Private LLM Deployments
Public LLM Characteristics
- Rapid deployment through existing APIs, with little to no infrastructure setup
- Broad general knowledge and strong performance on common business tasks out of the box
- Usage-based pricing tied to consumption (tokens, requests, or seats)
- Frequent model upgrades managed entirely by the provider
- Data typically processed on the provider's infrastructure, subject to the provider's terms
Private LLM Characteristics
- Deployment within an environment the enterprise fully controls (on-premises or private cloud)
- Ability to fine-tune the model on proprietary data, terminology, and workflows
- Full control over data residency, retention, and access logging
- Higher upfront investment in infrastructure, integration, and specialized talent
- Slower to update, since model improvements depend on the organization's own release cycle
Why Enterprises Choose Public LLMs
- Speed to value. Teams can integrate a public LLM into existing workflows within days, not months.
- Lower initial cost. There is no need to provision GPU infrastructure or hire a specialized MLOps team.
- Continuous improvement. Providers regularly release model upgrades, so capability improves without additional investment.
- Proven reliability at scale. Established providers operate infrastructure that has been stress-tested across millions of users.
Why Enterprises Choose Private LLMs
- Data sovereignty and compliance. Sensitive data financial records, citizen data, healthcare information, or trade secrets never leaves the organization's controlled environment.
- Customization depth. The model can be fine-tuned on internal documents, regulations, and terminology specific to the organization's sector.
- Predictable long-term cost at scale. For high-volume use cases, a private deployment can become more cost-efficient than ongoing per-token billing.
- Auditability. Every interaction, prompt, and output can be logged and reviewed to satisfy internal audit and regulatory requirements.
Practical Use Cases
Public LLM fits well for:
- Marketing content drafting and internal brainstorming
- Customer-facing chatbots handling general inquiries with no sensitive data exchange
- Employee productivity tools (summarization, meeting notes, translation)
- Rapid prototyping of AI features before committing to a larger investment
Private LLM fits well for:
- Government entities processing citizen data or classified information
- Financial institutions handling transaction records and regulated disclosures
- Healthcare providers managing patient records under strict privacy obligations
- Legal and contract review workflows involving confidential client information
- Organizations operating under Saudi data localization requirements, including entities regulated by the Saudi Data & AI Authority (SDAIA) and the National Cybersecurity Authority (NCA)
Challenges & Best Practices
Both approaches carry trade-offs that leadership teams should evaluate honestly rather than defaulting to whichever option is more familiar.
Public LLM challenges:
- Limited visibility into how the provider stores, uses, or retains submitted data
- Vendor lock-in and potential changes to pricing or terms of service
- Compliance risk when regulated data is inadvertently included in prompts
Private LLM challenges:
- Requires internal expertise (or a specialized consulting partner) to deploy, secure, and maintain
- Higher upfront capital expenditure for infrastructure and licensing
- Slower access to the latest model capabilities compared to commercial providers
Best practices for enterprises evaluating either path:
- Classify data before choosing an architecture not every workload requires a private deployment.
- Start with a hybrid approach where feasible: public LLMs for low-risk tasks, private deployment for regulated or sensitive workloads.
- Establish clear data governance policies before rollout, not after an incident.
- Involve legal, compliance, and IT security teams in the decision, not only engineering.
- Work with an implementation partner experienced in regional regulatory requirements to avoid costly missteps.
Frequently Asked Questions
What is the main difference between a public LLM and a private LLM?
A public LLM is hosted by a third-party provider and shared across many customers, while a private LLM runs in an environment the enterprise controls, with dedicated infrastructure and governance over the data.
Is a private LLM always more secure than a public LLM?
Not automatically. A private LLM gives the organization full control over data handling, but security still depends on how well the deployment is configured, monitored, and maintained. A poorly secured private LLM can be riskier than a well-governed public one. Which option is more cost-effective?
It depends on usage volume and workload type. Public LLMs are usually cheaper to start with, since there is no infrastructure to build. Private LLMs often become more cost-efficient at high, sustained usage volumes, but require greater upfront investment.
Can enterprises use both public and private LLMs at the same time?
Yes. Many organizations adopt a hybrid model — using public LLMs for general productivity tasks and private deployments for workflows involving sensitive or regulated data.
Do Saudi data protection regulations affect this choice?
Yes. Organizations handling regulated or citizen data should review requirements set by SDAIA and the National Cybersecurity Authority, since certain data categories may need to remain within approved environments, favoring private or locally hosted deployments.
How long does it take to deploy a private LLM?
Timelines vary based on scope, but organizations should generally plan for several weeks to a few months, covering infrastructure setup, fine-tuning, integration testing, and security validation.
Does a private LLM mean sacrificing model quality?
Not necessarily. Many private deployments are built on strong open-source or licensed foundation models, then fine-tuned on the organization's own data often improving relevance for domain-specific tasks even if raw general knowledge is narrower than the largest public models.
Who should be involved in deciding between public and private LLM adoption?
This decision works best as a joint effort between IT leadership, legal and compliance teams, and business stakeholders who understand the sensitivity and volume of the data involved not a decision left to engineering teams alone.
